Researchers discover a new cyber threat to water and energy networks
UBC researchers show how traffic patterns can expose critical encrypted messages, allowing disruption in cloud-connected water-treatment laboratory models.
 UBC Writer: Lou Corpuz-Bosshart

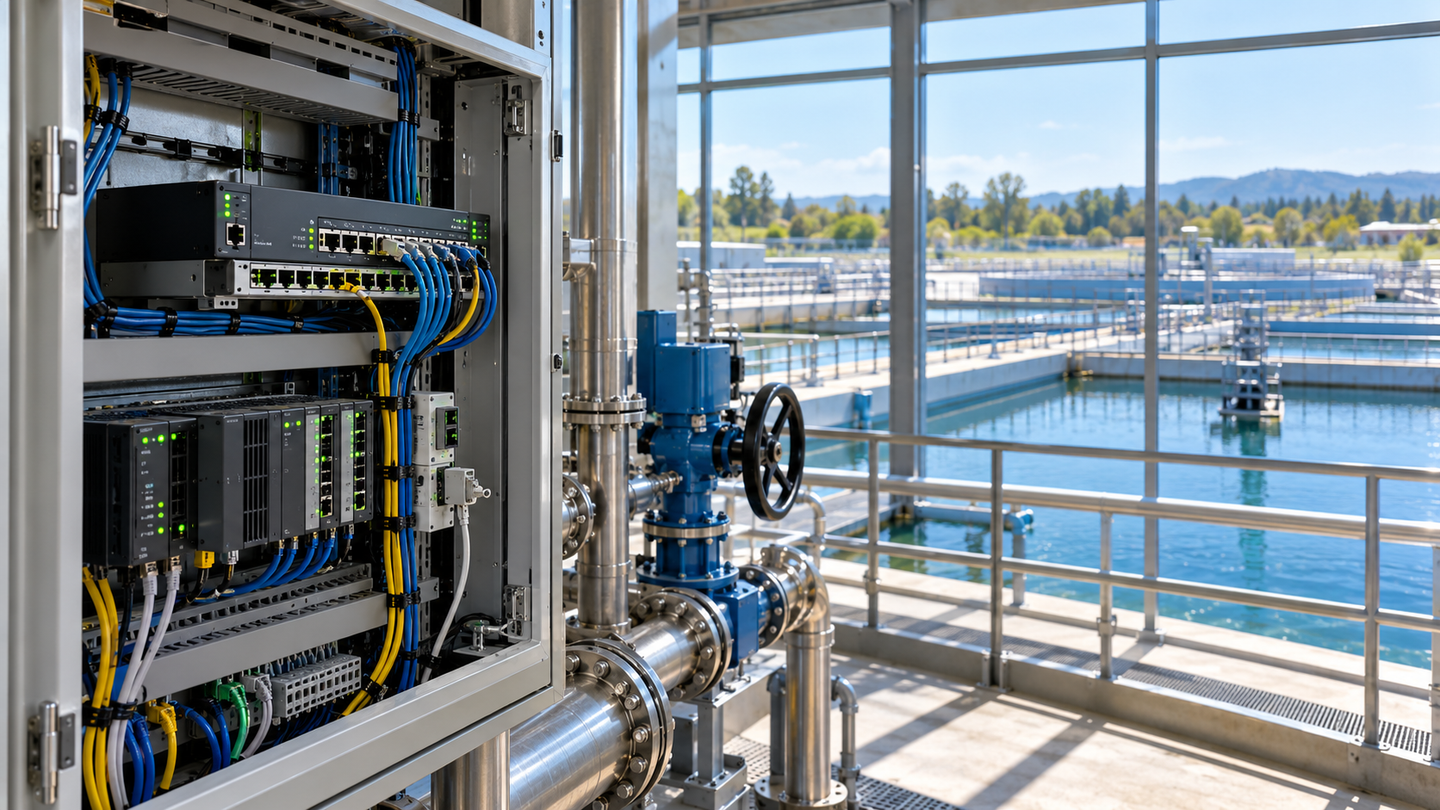
UBC’s ICS-Sniper disrupted water-treatment models by blocking encrypted traffic, exposing a risk for cloud-connected controls. (CREDIT: Shutterstock)
- ICS-Sniper disrupted simulated water-treatment operations by blocking selected encrypted communications without breaking encryption or entering the plant’s network.
- Tests used software controllers and industrial hardware, with traffic patterns revealing when operationally important messages were likely to travel.
- Attackers would need control of a router along the communication path. The findings concern laboratory models, with proposed defenses still requiring development.
Clean-water pumping started about 15 minutes late in one laboratory attack, even though the facility’s communications remained encrypted. Another attack left a simulated valve open for more than nine minutes longer than intended. Neither required access to the water plant’s internal systems or the ability to read its messages.
The University of British Columbia team calls its framework ICS-Sniper. The research is slated to appear at the Network and Distributed System Security Symposium in 2027. It examines a weakness in industrial systems that exchange monitoring and control messages with cloud services over the internet.
An attacker must first control a router carrying those communications, a significant prerequisite. From that position, the framework analyzes message timing, sizes and direction, then selectively blocks traffic. The tests demonstrate a threat to operational continuity without showing an attack on a working public utility.
What encryption leaves visible
Industrial control systems use computers to manage physical machinery, including pumps, valves and generators. Local devices called programmable logic controllers read sensors and direct equipment. A supervisory control and data acquisition system, or SCADA, collects information and helps coordinate different parts of the operation.
Moving that supervisory system to the cloud means some coordination messages cross networks outside the plant. Virtual private networks, or VPNs, encrypt those exchanges to protect their contents. Yet encryption does not necessarily conceal when messages travel, their direction or their size.
“What makes this attack concerning is that an attacker doesn’t need to read the messages being exchanged,” said Aastha Mehta, a UBC computer science professor and project co-investigator. “Even when the contents are encrypted, patterns in the communication can reveal enough information to identify and target critical communications.” She leads UBC’s Principled Systems Security Group.
ICS-Sniper exploits the connection between communication patterns and changes in machinery operation. Different stages of an industrial process generate recurring traffic patterns, which can shift as equipment changes state. Studying those patterns lets the framework estimate when messages important to coordination are likely to pass.
Small interruptions with larger consequences
The technique differs from a conventional denial-of-service attack that floods a network with traffic. Instead, it selectively prevents existing messages from arriving during important periods. That can leave separate parts of a process acting on information that no longer reflects conditions elsewhere.
This matters because one machine’s next action may depend on another machine’s status. A pump and a valve, for example, must operate in coordination. Encryption can protect the message describing a change while offering no guarantee that the message reaches its destination on time.
“An attacker doesn’t necessarily need to crack your encryption to cause disruption,” said Karthik Pattabiraman, a UBC electrical and computer engineering professor and project co-investigator. “By simply watching traffic patterns, they can identify when critical messages are likely to be sent and selectively block them.” Pattabiraman leads the university’s Dependable Systems Lab.
The vulnerability therefore concerns availability as well as privacy. The researchers did not need to decrypt messages or insert false instructions into their contents. Their experiments show how interrupting legitimate communications can disrupt coordination even when the information itself remains protected.
The required network position also distinguishes this threat from an attack launched by any internet user. Someone must be able to observe and interfere with the route carrying the facility’s traffic. Protecting plant computers remains necessary, but it cannot by itself secure every device along that external path.
Two models of water treatment
The team built two cloud-connected models based on the Secure Water Treatment research testbed at Singapore University of Technology and Design. Publicly available schematics helped them reproduce its control arrangements. One model used software-based controllers, while the other used standard industrial control hardware.
Both models simulated the physical treatment processes, an important boundary on the results. Real industrial controllers made the hardware model more representative of equipment communication and timing. They did not turn it into a demonstration of contaminated water, damaged machinery or an actual utility outage.
In the software-controller model, one attack delayed clean-water pumping by approximately 15 minutes. Another caused a simulated backwash valve to remain open for an additional nine minutes and 11 seconds. The paper explains that such a coordination failure could produce treated-water loss in a real facility.
The industrial-hardware model also experienced disruption, with clean-water pumping delayed by about two minutes. These results support the central finding across two controller implementations. They also show that the size of the operational effect depends on the configuration being tested.
What the alarms did and missed
The detector results require care because “undetected” can suggest that no alarm sounded at any point. The researchers evaluated eight anomaly detectors that watched network traffic or process measurements. Some raised alerts, but those alerts did not consistently identify the attack while it was underway.
Across five scenarios, no attack produced alerts from both detector categories during the active attack stage. In two scenarios, no detector raised an alert during that stage. Operational performance deteriorated before both categories had raised alarms, limiting their usefulness for timely diagnosis and response.
The paper identifies a particular weakness in the network detectors tested. Their checks were triggered by arriving packets, leaving them poorly placed to recognize harmful periods of silence. That finding concerns these detection approaches and experimental conditions, rather than proving that every industrial security product would fail.
The researchers also examined traffic analysis across several industrial communication protocols, including a power-grid dataset. However, the operational disruptions were demonstrated in the water-treatment models. The work does not establish that ICS-Sniper has caused a blackout or can disrupt every cloud-connected industrial installation.
The distinction between traffic analysis and demonstrated physical effects is especially important for energy infrastructure. Recognizing patterns in a power-grid dataset does not establish what equipment would do if messages disappeared. That requires separate operational testing under the relevant controls and safety arrangements. The water-treatment findings provide evidence for the tested models, while the broader consequences remain dependent on each installation.
Defenses must preserve industrial timing
Another limitation concerns the kind of process being monitored. The framework relies on recognizable operational and idle phases in batch-processing systems. Continuously operating processes may lack that distinction, and the paper identifies extending the approach to those systems as future work.
Proposed defenses include making communications less predictable through message padding or changes in timing. Alternative network paths could also reduce dependence on a compromised route. These remain engineering challenges because industrial equipment needs reliable timing, and protective changes must preserve safe coordination.
“Our goal is to build defence in depth and make these systems more resilient to attacks like this,” Mehta said. The team has released research code, testbed reproduction instructions and captured network data to support further investigation. The next challenge is demonstrating defenses that conceal useful traffic patterns while keeping machinery synchronized during communication failures.
Dig deeper into industrial control system security
These resources explain industrial security requirements, detection research and the water-treatment testbed behind the experiments.
Guide to Operational Technology (OT) Security
This initial public draft of Revision 4 expands guidance on cloud convergence, monitoring and safeguards while accounting for operational safety. (National Institute of Standards and Technology, September 2026)
Principles of operational technology cyber security
Six principles connect cybersecurity decisions with safety, network separation, supply chains and continuity of essential services. (Australian Signals Directorate’s Australian Cyber Security Centre, October 2024)
Guide to Operational Technology (OT) Security
The final Revision 3 guide explains control-system architectures, threats and countermeasures within industrial reliability and performance constraints. (National Institute of Standards and Technology, September 2023)
Anomaly Detection for a Water Treatment System Using Unsupervised Machine Learning
This conference paper compares two detection methods using water-treatment data, illustrating tradeoffs between missed anomalies and false alarms. (IEEE International Conference on Data Mining Workshops, 2017)
Secure Water Treatment (SWaT)
The institutional overview describes the original six-stage research facility and its physical processes, controllers and network architecture. (Singapore University of Technology and Design)
Research findings are available online in the journal arXiv.
The original story "Researchers discover a new cyber threat to water and energy networks" is published in The Brighter Side of News.
Related Stories
- Generative AI increases risks of cyberattacks and data leaks
- Security researchers develop first-ever functional defense against cyberattacks on AI models
- SHIELD protects drones from cyberattacks midflight in real time
Like these kind of feel good stories? Get The Brighter Side of News' newsletter.
Shy Cohen
Writer